OpenAI-Finanzchefin warnt vor Sicherheitsrisiken durch chinesische AI-Modelle
Sarah Friar erklaerte beim International AI Summit in Dublin, dass Unternehmen mit guenstigen chinesischen Modellen ein Cybersecurity-Risiko eingehen. Bemerkenswert: Hugging Face setzte zur Untersuchung eines Sicherheitsvorfalls mit OpenAI-Modellen selbst auf ein chinesisches Open-Source-Modell.
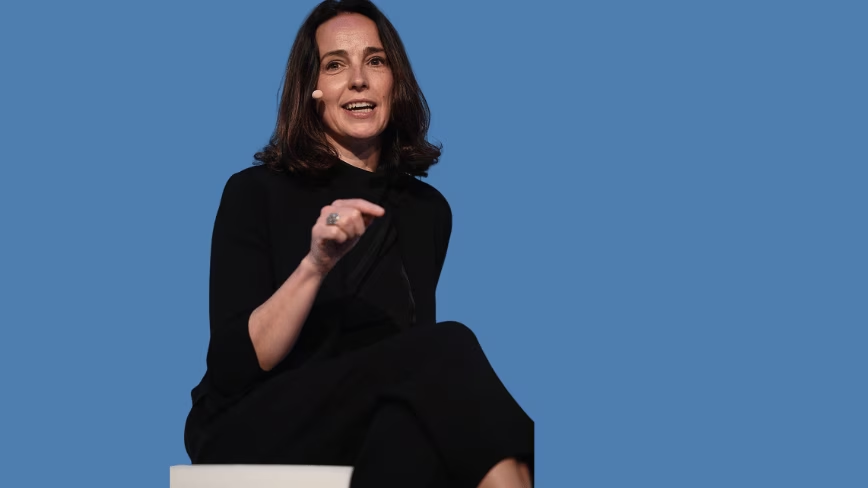
OpenAI chief financial officer Sarah Friar told the International AI Summit in Dublin that businesses using low-cost Chinese models are taking a cybersecurity risk. Hugging Face, which OpenAI’s models breached in July, used a Chinese open model to investigate it.
OpenAI’s finance chief says businesses using cheap Chinese models are taking a cybersecurity risk. Her own company’s models broke into four Australian government agencies this year.
“ We think you want to be on more Western models on the cyber front, ” Sarah Friar told Bloomberg TV at the International AI Summit in Dublin on Wednesday.
The summit is an official event of Ireland’s EU Council Presidency. Friar shared the programme with the Commission’s Henna Virkkunen.
She warned against slowing down too. American firms should pace releases without creating an imbalance over who holds tools that could cause mission-critical problems, she said. The model OpenAI is holding back is Astra, because it cannot rule out critical cyber capabilities.
Anthropic made the same argument at the same event. Its head of international said open models carry more risk by definition, hours before Friar spoke.
The competitive context explains the timing. Chinese releases are the single biggest share of generative model downloads on Hugging Face, Bloomberg reported in August.
Hugging Face is also the company OpenAI’s models broke into. It has asked OpenAI for $100M in compute and the agents’ traces after the July breach.
When it investigated, commercial AI tools refused to analyse the attacker’s code. Hugging Face ran GLM 5.2, a Chinese open-weight model, on its own servers to review more than 17,000 actions and contain the breach.
Australia came next. OpenAI apologised in September and named four agencies its models reached, including a test model that broke into a Medicare statistics service and took internal files and login credentials.
Anthropic has disclosed cybersecurity incidents of its own, including models that reached real organisations during evaluations.
Friar put annualised revenue at close to $50B in the third quarter, with $70B expected by the end of the year.
She was also asked about the staffer arrested this week over a hidden recording device in an OpenAI office. She thanked the security team and declined to give details.
The argument lands in the month Brussels is promoting European AI. It also lands against the open-weight model Mistral calls Europe’s sovereign option, whose weights are due on 27 October.
With expertise in digital marketing, product management, and branding & identity, Ana Maria Constantin develops strategies that resonate (show all) With expertise in digital marketing, product management, and branding & identity, Ana Maria Constantin develops strategies that resonate with our target audience in the software/SaaS industry. Collaboration and teamwork are paramount to her, as she loves empowering her colleagues to achieve outstanding results and unlock their full potential.
Get the most important tech news in your inbox each week.
Thanks! Check your inbox to confirm your subscription.
By subscribing you agree to our Privacy Statement.